Concept dictionary
Adversarial Attack
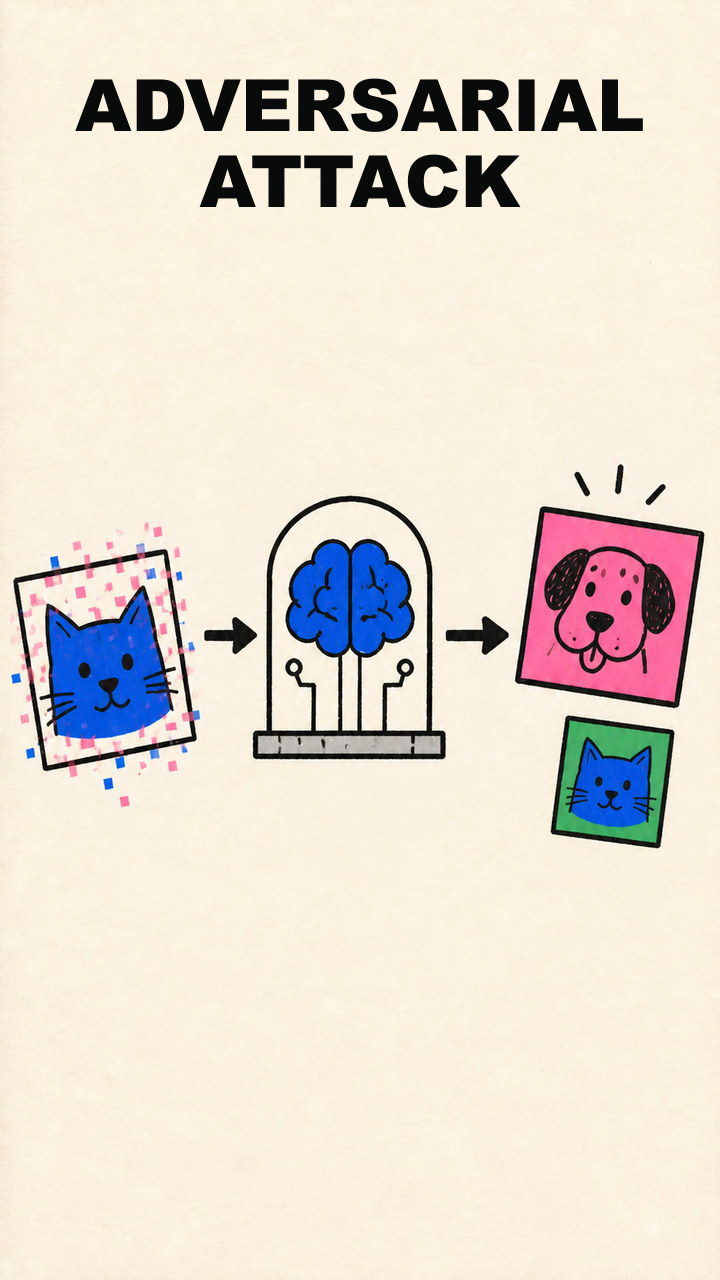
An adversarial attack is a deliberate attempt to manipulate an AI system's inputs, data, environment, or interfaces so it produces an incorrect, unauthorized, or harmful result.
- Review state
- Needs review
- Freshness
- Current
- Version
- 2
Also called
- Adversarial Attack
- Adversarial AI Attack
Remember it this wayThe input is designed to make the system fail.
In plain language
An attacker looks for weaknesses in what the system sees, trusts, or can access. The attack may target the model directly or the larger application around it.
Why it matters
Ordinary accuracy tests do not establish security under deliberate pressure. Systems need threat modeling, access controls, monitoring, and adversarial testing.
Example
An attacker makes a small, carefully chosen change to an input so an automated classifier assigns the wrong category.
Common misconception
Adversarial attack is not another name for constructive disagreement or red-team review. It describes an attempt to cause failure or misuse.
Related terms
Sources
- NIST AI 100-2 E2025, Adversarial Machine Learning: A Taxonomy and Terminology of Attacks and Mitigationsofficial taxonomy covering adversarial machine-learning attacks, attacker goals, and mitigations.
Learn more
- Contrast the attack with defensive [[red-teaming|Red Teaming]].